The colleague at the next desk may have ChatGPT open in a tab, on a personal account. This morning they pasted in the minutes of a client meeting to get a clean summary. They saved twenty minutes, and nobody will know: not you, not the IT department.
This is what we call Shadow AI. In French-speaking Switzerland, 27% of people who use AI at work do so without their employer’s approval, according to the Qualinsight study published in spring 2026. And that figure only counts those who are willing to admit it.
In this article, we look at what Shadow AI is, why it is spreading, what risks it creates and how to manage it without slowing down the people who benefit from it. What we have learned in our assignments fits in one sentence: you need a framework and tools, and one does not work without the other.
Do you use AI tools at work that your organisation does not provide? No study measures this across Switzerland yet. We are running an anonymous survey of 7 questions, open until 31 December 2026, with results published on 15 January 2027.
- Shadow AI is the use of AI tools at work without the company’s approval or control: a personal ChatGPT account, a browser extension, a bot that records meetings.
- It spreads because the time saving is real, and because the company often provides neither clear rules nor a suitable tool. In French-speaking Switzerland, 49% of employees say their organisation has no clear rules on AI, and 79% have never been trained.
- The main risk: data about clients, employees or confidential information leaving for services hosted outside Switzerland, with no safeguards.
- Banning does not stop the usage, it makes it invisible. Ignoring lets the risk build up unseen.
- The approach that holds: a framework (governance, AI policy) and tools (AI gateway, approved tools, training). Without a framework, you create risk. Without the right tool, people work around you.
What is Shadow AI?
The term comes from “Shadow IT”, the software employees install without going through the IT department. Shadow AI is its AI version: the use of artificial intelligence tools outside what the company has approved and knows how to manage.
A few examples, drawn from ordinary situations:
- a lawyer pastes a contract clause into her personal ChatGPT account to reword it
- an HR manager has a free chatbot summarise annual appraisals
- a sales rep installs a browser extension that drafts his emails, and therefore reads every email he opens
- a new employee invites to Teams meetings the recording bot she used in her previous job
The tool is not the problem, the framework around its use is. The same lawyer can make exactly the same request in a company tool, under contract, with data processed and stored in Switzerland or the European Union: that is managed use.
With Shadow IT, the company lost control of a piece of software. With Shadow AI, it loses control of its data: every request to an external tool takes with it the text, file or conversation entrusted to it.
Why it happens
Nobody does Shadow AI out of a taste for risk. The reasons are almost always the same.
The time saving is real. ChatGPT has existed for almost four years. Since then, the models have improved a great deal, and their “harnesses” even more: the environment around them that gives them access to your files, to the internet, to pre-packaged capabilities (the “skills”) or to agents that chain tasks together on their own. Used well, these tools save a lot of time. When the gain is that clear, people accept a risk they do not always measure.
There are no rules. In the Qualinsight study, nearly one employee in two in French-speaking Switzerland says their organisation has no clear rules on AI. Without instructions, everyone sets their own limits.
There is no tool, or not the right one. In a survey carried out for Microsoft in the United Kingdom among 2,000 employees, 71% say they have already used unapproved consumer AI tools. Their top two reasons: habits formed in private life (41%) and the lack of a tool provided by the employer (28%).
These figures come from the UK. We are building the Swiss equivalent: take one minute to answer our anonymous survey, open until the end of December.
The Microsoft Copilot case
Many companies have chosen Microsoft 365 Copilot to give their teams AI built into their work environment. The choice is consistent. Yet a few months after deployment, some employees keep working in ChatGPT or Claude with a personal account. In our assignments, three reasons come up:
- the uses are not quite the same: each tool has its own functions, and habits formed elsewhere do not carry over with one click
- some advanced functions, such as Copilot Cowork, which works directly on your files, are billed by usage and often not activated (we explain this billing model in our article on the cost of Copilot Cowork)
- above all, many employees think Microsoft Copilot is “less powerful”. Yet it relies on the same families of models as its competitors: those of OpenAI and, for some functions, those of Anthropic
That last point says a lot about Shadow AI: people often work around the official tool out of unfamiliarity, not ill will. And unfamiliarity is addressed through training.
What management does not see
Management and teams do not look at AI from the same place. In an Accenture survey carried out at the end of 2025 among nearly 2,000 executives and employees in Europe, 94% of executives consider their teams’ basic training sufficient. Only 27% of employees share that view. And according to the KPMG and University of Melbourne study published in 2025, more than half of Swiss users admit having already used AI against their company’s rules, for example by uploading sensitive data into free tools.
In training sessions, we see it at every round of introductions: what people declare at the start of the day is far from what they say at the end.
In Switzerland, 86% of employees use AI at work according to EY’s European barometer (2025, 500 Swiss employees surveyed). Among the cybersecurity leaders surveyed by Gartner in 2025, 69% suspect or have evidence that employees are using prohibited AI tools. And among the 600 organisations that suffered a data breach studied by IBM the same year, one in five attributes it to Shadow AI.
The risks, in order of priority
Not all uses are equal. Rewording a text meant for the public with ChatGPT is not a problem. Pasting a client file into it is. Here are the risks to look at first.
-
Critical
Leak of personal or confidential data
An HR file or a client contract pasted into a free tool whose terms allow the data to be reused.
What reduces it -
Critical
Non-compliance with the FADP (Swiss data protection law)
Client data sent to a service hosted outside Switzerland without contractual safeguards.
What reduces it -
Critical
Breach of professional or business secrecy
A patient or client file, or a manufacturing process, handed to an external tool.
What reduces it -
High
Prompt injection
An email or a document contains hidden instructions that the AI assistant carries out without the user knowing.
What reduces it -
High
Malicious AI extensions and apps
An “AI assistant” extension that siphons off conversations and visited pages.
What reduces it -
High
Unvetted agents, skills and connectors
A connector installed on one’s own that gives an agent access to email or files.
What reduces it -
High
Personal accounts outside any control
No company sign-in, conversations shared via public links, data that leaves with the employee.
What reduces it -
High
Meetings recorded without participants knowing
A note-taking bot invited without the others knowing, clients included.
What reduces it -
High
Leak of source code and intellectual property
Code or drawings pasted into a consumer assistant to be fixed.
What reduces it -
Moderate
Wrong answers reused without checking
A figure invented by the AI that ends up in a client proposal.
What reduces it -
Moderate
Hidden costs
Individual subscriptions paid out of pocket or on expenses, with no overall view.
What reduces it
On the legal side, the Swiss Federal Act on Data Protection (FADP, known in French as nLPD) does not ban AI. It governs what is done with personal data: its security, its transfer to processors, its transmission abroad. The Federal Data Protection and Information Commissioner (FDPIC) has been pointing out since 2023 that the law applies directly to processing carried out with AI. A Swiss particularity: the fines provided for, up to CHF 250,000, target first and foremost the person who acted intentionally, not the company. A well-meaning employee can therefore be exposed personally, and a manager who failed to prevent the offence can also be held liable. One more reason to give everyone a clear framework.
Ban it, ignore it or manage it
Ban it. Blocking ChatGPT on the company network takes five minutes. The employee then takes out their phone. The usage does not disappear, it becomes invisible. In a Software AG survey of 6,000 employees in the United States, the United Kingdom and Germany, 46% say they would carry on even if it were banned.
Ignore it. Letting it happen means letting everyone decide alone what can leave the company, and letting the risks in the table build up unseen.
Manage it. This means acknowledging that the usage exists and brings something, then giving it a framework and tools. It is also the approach of the NCSC, the UK’s cybersecurity agency: understand why people turn to these tools, and seek to reduce the risk rather than eliminate it.
A framework without tools, and people work around it because the gain is too strong. Tools without a framework, and you are no longer compliant. The two move forward together.
Managing it in practice: a framework and tools
Governance, policy, gateway, training, audit: these are the workstreams we carry out with our clients in our AI consulting assignments.
Governance: who decides what
Before the rules, you need to know who sets them and who keeps them alive. In a small or mid-sized company, a small team is enough: management, IT, a business representative and, if possible, someone who knows data law. It decides which tools are authorised and for which uses. And it reviews its choices regularly, because the tools change very fast.
The AI policy: short and readable
The policy translates these decisions for everyone. It answers three questions: which tools can I use, with which data, and what never leaves the company. Two pages that people read are worth more than twenty that nobody opens.
The AI gateway: a single entry point
This is the least familiar tool, and yet it solves a good part of the problem. An AI gateway sits between your employees and the AI models. All requests go through it, much as a company’s calls go through its switchboard.
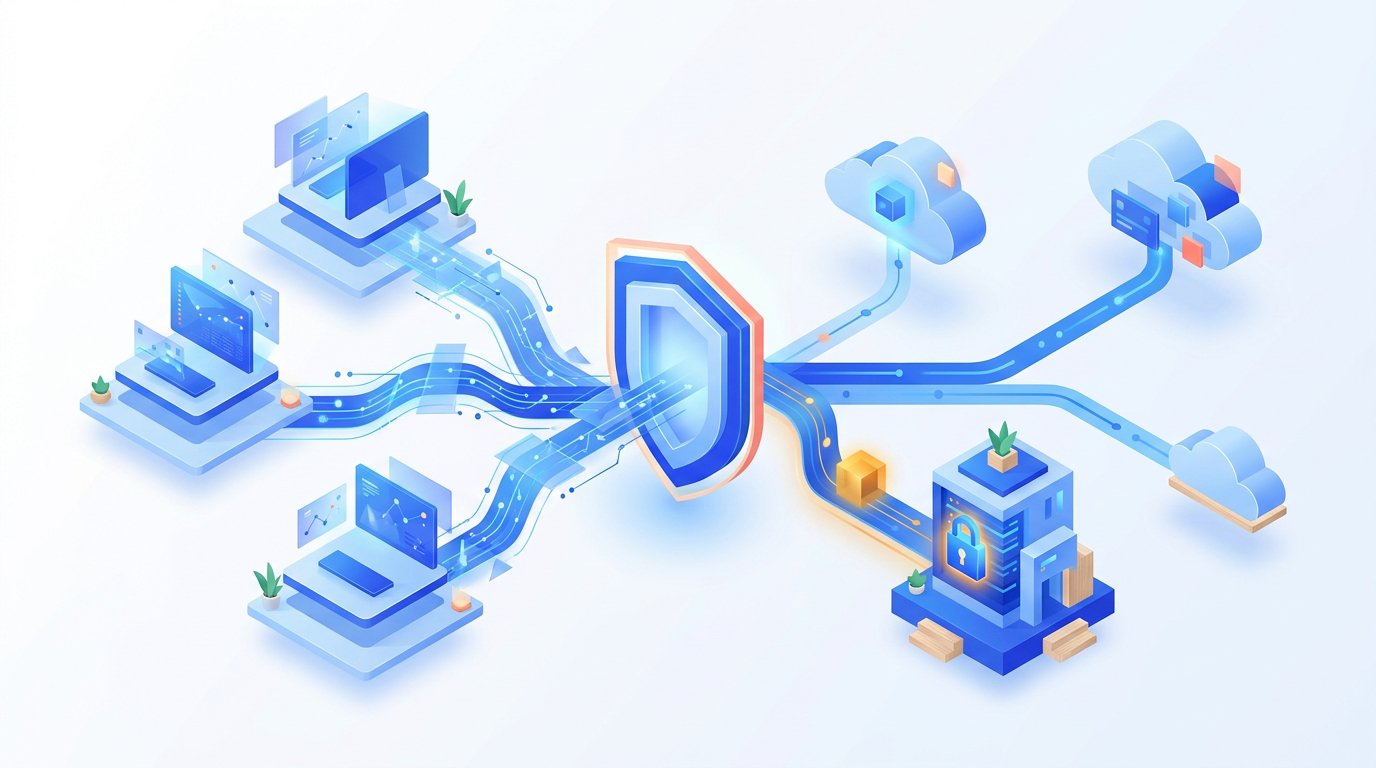
What it allows:
- routing each request to the right model: a question containing sensitive data goes to a model hosted by you or in Switzerland, a general search to a major market model
- filtering personal data before it leaves
- blocking some attacks, such as prompt injection, by spotting suspicious instructions before they reach the model
- tracking usage and costs, by team, with quotas
- switching models when a better one comes out, without changing users’ habits
The effect on Shadow AI is direct: teams have access to the best models, in a controlled setting, and the main reason to work around the rules disappears. A gateway still cannot see personal accounts used outside the company network. That is why it only works together with the policy and training. It is one of the topics we cover in our integration projects.
For a one-off need, our free Anonymiser removes personal data from a text directly in your browser, before you entrust it to an AI.
Training: what holds the rest together
The Microsoft Copilot example shows it: a good tool that is poorly mastered gets worked around. Training means explaining why certain data must not leave, and showing what the tools provided can do. In the Qualinsight study, 63% of trained people use AI every week, against 34% of the others: training does not hold back usage, it grows it within the right framework. Our AI training starts from the tools your teams already use every day.
Audit and integration: start from what exists
Before choosing tools, it is worth looking at what is already happening: which tools, for which tasks, with which data. An anonymous, no-sanction internal survey gives a truer picture than any network block. You then keep what works, replace what exposes you, and build the right tools into the teams’ daily work.
Choosing tools and writing rules is easier when you know where you are heading. With Journey to AI, in four to six weeks we take stock of how AI is used in your organisation and of your AI maturity, then build a prioritised roadmap with you. Discover Journey to AI
Don’t overdo it
Managing does not mean monitoring every click. The aim is visibility: proportionate logging, rules that are understood, and an open door for questions. A team that can say “I used this tool, is that fine?” without fearing a reprimand no longer has a reason to hide its usage.
Zero risk does not exist. The goal is for the approved tool to be good enough that nobody wants to do without it.
FAQ
Is Shadow AI illegal in Switzerland?
Should we ban ChatGPT at work?
How do I know whether my employees are using AI without telling me?
Is Microsoft Copilot enough to solve the problem?
Who is responsible in case of a leak?
Is an AI policy enough?
What does an AI policy contain?
What is an AI gateway?
What is prompt injection?
Take stock of how AI is used in your organisation: audit and consulting · AI training · contact us.
Sources
- Qualinsight × SwissTranscript, “AI at work in French-speaking Switzerland 2026” (1,030 employees, fieldwork March 2026)
- EY, European AI Barometer 2025 (8 July 2025, including 500 Swiss employees)
- Accenture, Pulse of Change (survey Nov.-Dec. 2025, about 1,070 executives and 900 employees in Europe), via AWP / cash.ch (15 January 2026)
- KPMG and University of Melbourne, “Trust, attitudes and use of AI” (2025), Swiss results via Netzwoche (5 May 2025)
- Microsoft UK, “Rise in shadow AI tools raising security concerns for UK” (13 October 2025, 2,003 employees)
- Gartner, press release of 19 November 2025 (302 cybersecurity leaders)
- IBM, Cost of a Data Breach 2025 (30 July 2025, 600 organisations)
- Software AG, survey on unauthorised AI (September 2024, 6,000 employees in the US, UK and Germany), via Unleash
- NCSC (United Kingdom), “The hidden risks of shadow AI” (7 September 2026)
- Federal Act on Data Protection (FADP, nLPD), art. 8, 9, 16, 61 and 64
- FDPIC, “Current data protection legislation is directly applicable to AI” (9 November 2023, updated 8 May 2025)
- Microsoft Learn, “AI gateway capabilities in Azure API Management”